Short answer
A FortiGate checks every connection against ordered firewall policies matched on source, destination, user and application. If a policy allows the traffic, the attached security profiles inspect it for intrusions, malware and blocked categories. Allowed traffic passes and is logged; anything unmatched is denied by default.
Updated 2026-09-21 · 4 min read
What happens to a packet
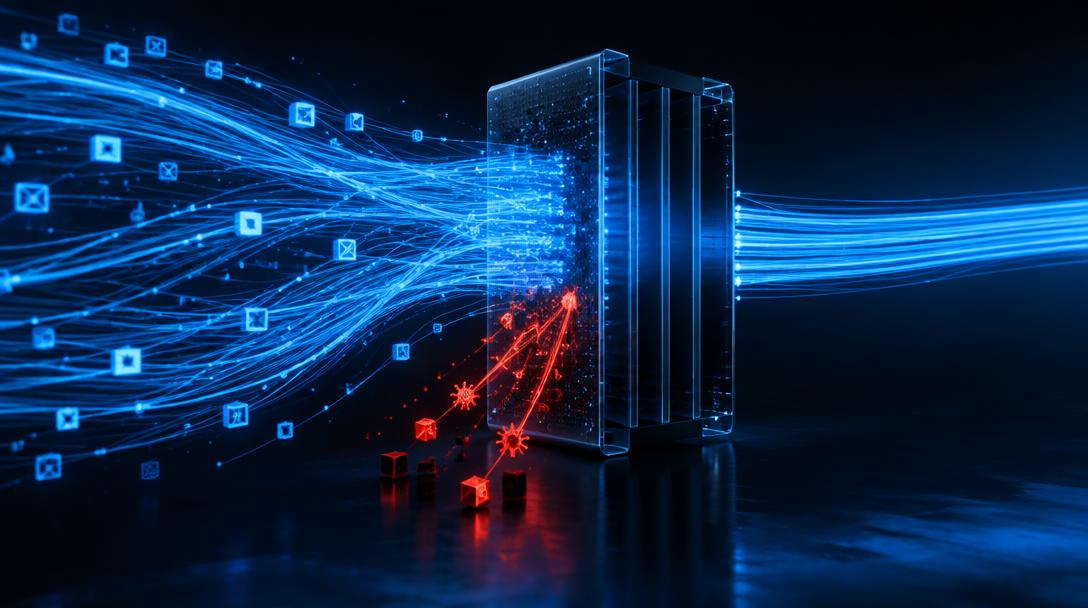
- The connection arrives on an interface and is matched against the policy list, top to bottom
- The first matching policy decides allow or deny — nothing matching means deny
- Allowed traffic runs through the attached profiles: IPS, antivirus, web filter, application control
- Encrypted traffic is decrypted for inspection if SSL inspection is enabled, then re-encrypted
- The session is logged, so you can see later what was allowed and what was blocked
Why policy order matters
Policies are evaluated in order, so a broad allow rule near the top will mask the tighter rules below it. Most firewalls we review have accumulated overlapping rules over the years — tidying that order is often the quickest security improvement available.
Hardware acceleration
FortiGate models include purpose-built security processors that handle inspection in hardware. This is why a small FortiGate keeps its throughput with inspection enabled, where a general-purpose appliance slows sharply.
Related questions
- Does SSL inspection slow things down?
- It adds load, which is why sizing matters. On the right model with hardware acceleration the impact is small for typical office traffic.
- How often should policies be reviewed?
- At least annually, and whenever an application or site changes. Old allow rules are the most common weakness we find.
Hardware for this
The ranges below cover what this article describes, supplied in the UK with lead times confirmed before you commit.